01
SCAN
Inspect npm metadata, the published tarball and OSV advisories.
Console// illustrative output
- $ npm install lodash
- > resolving registry metadata
- > inspecting published tarball
Security layer for autonomous agents
Dependency security for AI agents. Signed evidence, optionally anchored on Solana.
// capability summary · live per-deployment counts in the console
The problem
AI agents and modern applications rely on thousands of open source packages. A single malicious or compromised dependency can lead to fund loss, data theft, or complete system takeover.
Signed security evidence
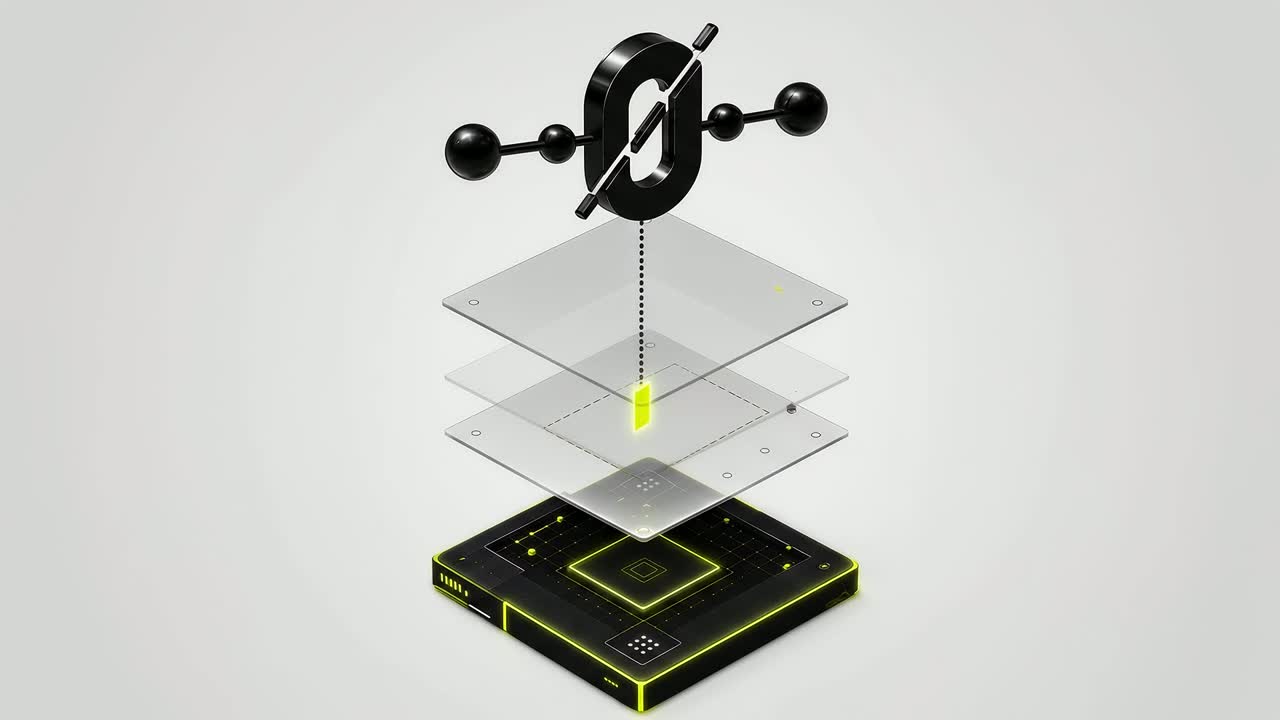
Three local scanner roles sign package findings. Exportable proof bundles let anyone verify those signatures and match the evidence against a commitment recorded on Solana Devnet.
// simulated live telemetry · prototype values
How it works
Every package you name is scanned and signed before it installs. Signed evidence proves what was inspected and that it has not been altered since — it does not prove the verdict is correct, and the Solana anchor is optional.
01
Inspect npm metadata, the published tarball and OSV advisories.
02
Three local scanner roles sign their findings; policy returns ALLOW, REVIEW or BLOCK.
03
The firewall enforces the verdict before npm runs. Anchoring is optional.
Built for the next generation
Ship evidence you can hand to a reviewer: a signed proof bundle, an optional Solana Devnet anchor, and a firewall that holds the verdict before npm runs.